Clients move to a new address or change their name. Company clients lose directors, change hands or start trading in another country.
None of that reaches the file on its own. The file still describes each client as they were on the day you approved them.
Out-of-date files tend to surface all at once, often when a new rule changes what a complete file must hold. Every one of those files then needs something from a client who thought the paperwork was finished. Some of those clients will never answer.
Until a client’s file is complete, their next request, such as a new account, may be held up. KYC remediation brings existing client files up to the standard your rules require today.
You find what is missing or outdated, get it, check it and record the result. The Financial Action Task Force (FATF) standard covers existing customers too, based on materiality and risk (Recommendation 10).
No one can call an old file incomplete until someone writes down what complete means today. A company file needs a registry extract and details of its beneficial owners.
For a US bank, a complete file starts with what its customer identification program collects before the account opens.
From 10 July 2027, one EU list of identity details applies in every member state, including place of birth and nationality (Regulation (EU) 2024/1624, Article 22). National lists differed: French firms already record the place of birth (Code monétaire et financier, R561-5), but that article does not list nationality. Check which items your old files lack before you ask clients for them.
Clustdoc lets you keep that standard as a customizable KYC onboarding checklist. Your team checks every old file against it.
The file of a politically exposed person (PEP) whose source of wealth was never established goes near the top. EU rules require firms to take adequate measures to establish it in every PEP relationship. An old utility bill in a low-risk file can wait.
The date of the last check, if any, and the quality of the data also count (Interpretive Note to Recommendation 10). A workable order: risk rating first, then the last review date, then the gap size.
AMLA, the EU’s anti-money laundering authority, sent the European Commission final draft standards on customer due diligence in a report dated 30 September 2026. The Commission has not adopted them yet.
Under the draft, firms would bring existing files up to the new standards by risk. The EU’s maximum time between updates would set the deadline, counted from when the standards enter into force.
A remediation request is not a second onboarding. For a company client’s beneficial owners, US banks and other covered institutions need only update what has changed (FinCEN CDD FAQ B.20).
Confirming a known owner’s new address may take only a call to the company. A new owner needs full checks.
Many firms ask for a new ID when the old one expires. By default, that is not needed in Australia or under AMLA’s June 2026 draft guidelines on ongoing monitoring.
Expiry alone does not change who the client is. So decide per document type, up front, whether expiry calls for a new copy.
Our directory and data mapping feed the contact and company data you hold into the update workflow. Your team does not type the same data twice.
A second KYC request can read like suspicion to a long-standing client. So say in one line why you ask again: your rules require up-to-date client information.
Name each item, mark what can simply be confirmed, and give one deadline and what follows it. A client’s confirmation can be enough, though AMLA’s draft guidelines may expect it to be checked, depending on the risk.
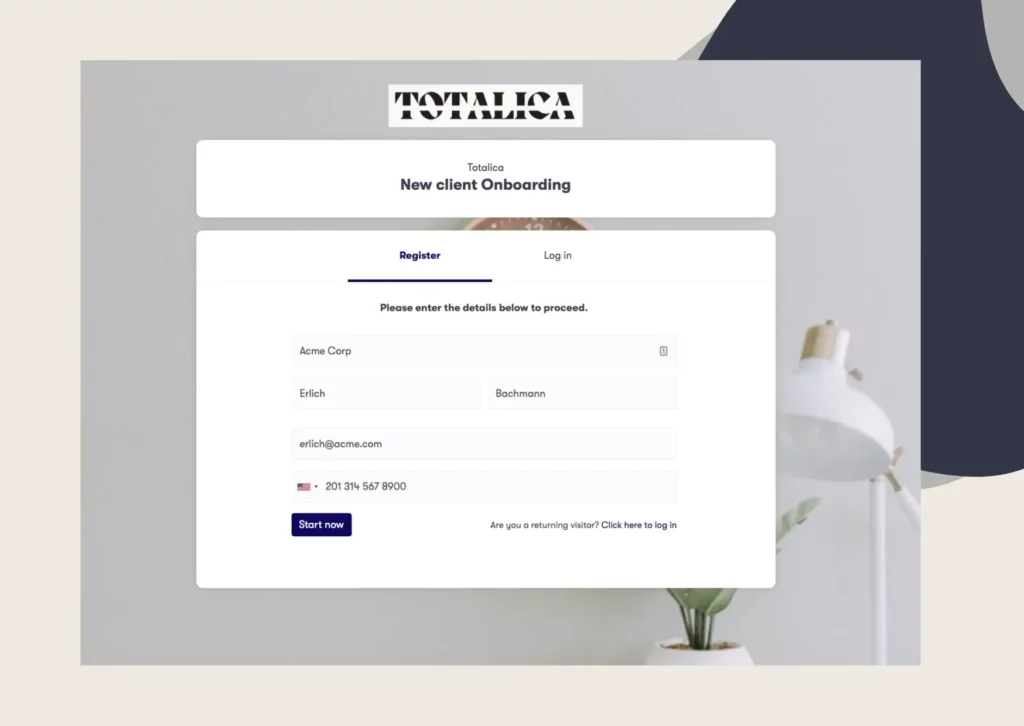
Our client portal can be set to login-only, so only existing clients can open it. Automatic reminders follow by email, SMS or both, on the trigger and timing you choose. Unresolved steps can be escalated automatically.
If the checks cannot be completed, the FATF standard is to end the relationship (Recommendation 10). EU firms must also end it, today and from 10 July 2027 (Directive (EU) 2015/849, Article 14(4); Regulation (EU) 2024/1624, Article 21).
In France, a firm that cannot keep its client information up to date neither starts nor continues the relationship (L561-5-1 and L561-8). US bank rules leave this to each bank’s procedures, which should cover insufficient or inaccurate information (FFIEC).
Put these in your policy before the first request:
This is general information, not legal advice.
Each reply, such as a new passport, is accepted or returned with a reason. If the answers change the picture, as a new owner would, re-rate the client.
Record what was asked, what came back, who checked it and what was decided. A record of actions and decisions, with supporting documents and reasons, becomes an EU requirement on 10 July 2027. It covers ended relationships too (Regulation (EU) 2024/1624, Article 21(3)).
That record builds up in our audit trail as the file moves: what the client sent, what the reviewer decided and when.
Is this a one-off fix, or the regular update every file needs? A KYC refresh, also called a periodic review or KYC review, keeps a file that passed the KYC process up to date.
|
|
KYC refresh |
KYC remediation |
|---|---|---|
|
What it does |
Keeps a complete file current |
Brings files up to today’s standard |
|
What starts it |
The review date, or a change you learn about |
An audit or exam finding, a new rule, an acquired client book |
|
How often |
By risk, within any legal maximum |
Once, to a deadline |
|
Client is asked to |
Confirm what you hold, send changes, replace expired documents per your policy |
Send whatever is missing |
The KYC refresh process uses the same steps, a few files at a time. Our platform runs it as a KYC renewal campaign that requests refreshed documents and keeps the KYC history together.
Once the backlog is cleared, ongoing due diligence keeps files from falling behind again.
For US banks, an event sets off the update, not the calendar (FFIEC). Banks may still choose periodic reviews by risk.
Under US rules, this sits inside ongoing monitoring. On a risk basis, banks maintain and update customer information, including the beneficial owners of company clients (31 CFR 1020.210(a)(2)(v)(B)).
EU rules add time limits from 10 July 2027. Firms must review a file when the client’s circumstances change, and update it at least yearly under enhanced checks (Regulation (EU) 2024/1624, Article 26). For other clients, the limit is five years.
In France, firms must keep their knowledge of the relationship appropriate and up to date while it lasts (R561-12). Your policy then sets the periodic KYC refresh cycle for each risk level, within those limits.
A letter to a client comes back undelivered. Other early signs:
Unexplained activity or negative news may call for a new rating too. If your policy asks for a current document, our data quality management can request a new one once the copy expires.
A review date can sit years away, while a client company changes hands next month. Perpetual KYC (pKYC), also called continuous KYC, updates a file as soon as monitored data shows a change.
That could be a new director in a company registry or a new sanctions listing. Data feeds and monitoring tools raise those flags.
The EU limits above apply here too, from 10 July 2027. A client whose data never raises a flag still needs a dated update.
If you already use a monitoring tool, we can build the update workflow around it. Its flag can then start that workflow through our REST API.
Pick one client group to start with and book a demo call. We will show how its update requests and reminders run in Clustdoc.
KYC remediation is a one-off project to bring existing client files up to today's standard. The firm finds what is missing or outdated, gets it, checks it and records the outcome. Audit or exam findings, new rules and acquired client books can trigger it.
A KYC refresh is the regular update of a file that was complete when last checked. It happens on a review date set by risk, or sooner when something changes, such as a new owner. The client confirms what you hold and sends changes.
Perpetual KYC updates a client file when monitoring shows a change, not on a fixed review date. US bank rules do not require it. In the EU, the maximum gaps between updates apply to it from 10 July 2027, so firms keep a dated backstop.
If the checks cannot be completed, the FATF standard is to end the relationship and consider a suspicious transaction report. EU and French rules say the same.
Under EU rules, one group is exempt from this exit rule: notaries, lawyers and other independent legal professionals, auditors, external accountants and tax advisers. The exemption applies only while they work out a client's legal position or act for the client in, or concerning, court proceedings. That includes advice on starting or avoiding such proceedings.
From 10 July 2027, it never covers a professional who takes part in, or gives legal advice for, money laundering or terrorist financing. Nor does it cover one who knows the client seeks such advice (Regulation (EU) 2024/1624, Article 21(2)).
Still stitching emails, files, and approvals together?
Clustdoc gives teams one place to run client-facing work, boost customer engagement and increase compliance.
Claire writes about customer onboarding, digital processes, and the day-to-day challenges faced by operations teams. At Clustdoc, she focuses on practical insights: how organizations collect information, guide customers through complex steps, and improve service delivery with automation.