Where will the file with every employee's bank details live once your new payroll provider has it? That question often comes up only after the contract is signed. By then, nobody has checked who at the provider can open the file or what happens if it goes out of business.
If the provider leaks it, any breach notices to your employees go out under your company's name. If it shuts down, your staff may not get paid on time while you find a replacement.
Neither the signed contract nor the provider's promise answers those questions.
Types of Vendor Risk to Check
Many vendors never see anything sensitive, so the first job is finding the ones that do. A vendor risk assessment is the check you run on a supplier before you sign and while you work together. It asks what could go wrong if the vendor fails, leaks data or breaks a rule.
It also asks whether the vendor's controls are good enough to accept. Some teams call it a third party risk assessment or a supplier risk assessment.
Every vendor gets a light check, such as confirming the company exists. Would losing this vendor stop your work or affect your customers? Will it hold personal data, client files or access to your systems?
A yes to either means a full check across the five areas below.
Security and Data Protection
Start with what the vendor can reach: your systems, client files, or staff and customer data. For software and IT providers, the IT team often runs this part as a separate vendor security assessment.
Ask for an independent security audit, such as a SOC 2 report or an ISO/IEC 27001 certificate. Check that its scope covers the service you buy.
Its incident response plan, data breach history and encryption standards matter too. Vendors can submit all of these through Clustdoc's vendor due diligence checklist template.
Under the EU's GDPR, a vendor that handles personal data for you is a processor. Article 28(1) lets you use only processors that give sufficient guarantees of appropriate technical and organizational measures.
Those measures then go into the data processing agreement. It must also say the vendor will return or delete your personal data when the work ends, as you choose (Article 28(3)(g)).
Compliance, Licenses and Reputation
A vendor that loses its license halfway through a contract may no longer be allowed to do your work. So check the license the work needs, such as a payment or insurance license, against the regulator's public records.
The company behind the license needs checking too: whether it is active and in good standing, who runs it and who owns it. These are the same company record, director and beneficial owner checks used in KYB verification. Screen the company and its owners against sanctions lists as well.
Search court records, enforcement actions and the news too, since they show problems a vendor will not mention.
Financial Health
A supplier that passes every security check may still be close to running out of cash. Ask for the latest financial statements, and for vendors you depend on, add a credit report.
Where company accounts are public, you can also pull the filed accounts from the company registry. Check that the statements belong to the company that signs your contract, not a parent or sister company.
Then look for warning signs: accounts filed late, losses year after year, or one customer making up most of the vendor's sales.
Operations and Continuity
What happens to your payroll run if one vendor's systems stop for a day? The vendor's business continuity and recovery plan should answer that. Check when it was last tested and who you call during an outage.
Plan the exit before you need it: how you get your data back and move the work to another vendor.
In the EU, the Digital Operational Resilience Act (DORA) has applied since 17 January 2025 to banks, insurers, investment firms and other financial firms it covers. For ICT (information and communication technology) services that support critical or important functions, those firms need exit strategies (Article 28(8)). The plans must be documented, tested and reviewed from time to time.
Subcontractors and Concentration
The company you sign with is often not the only one that touches your data. Which subcontractors and hosting providers deliver part of the service?
Under GDPR Article 28(2), a processor needs your prior written approval before it brings in another processor. The approval can name each one or cover them in general. With general approval, the vendor must tell you before it adds or replaces one, so you can object.
One outage can also stop several vendors at once. That is vendor concentration risk, as when two vendors run your payroll and HR tools on the same hosting provider.
Firms covered by DORA must also check for concentration before signing for those ICT services (Article 29). Would the provider be hard to replace? Would they hold several such contracts with it, or with closely connected providers?
Vendor Risk Assessment Questionnaire: Questions and Proof to Request
Keep the questionnaire short for low-risk vendors and send the full set to vendors that hold data. A full set covers the four areas our due diligence questionnaire template uses: corporate and legal, financial, operational, and compliance, security and data.
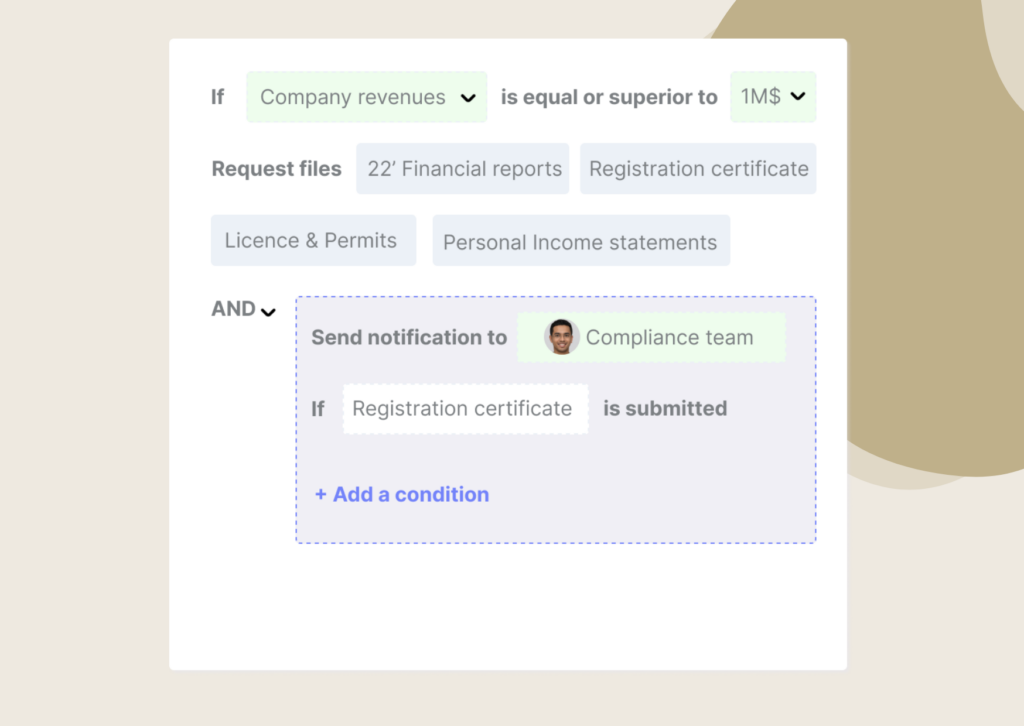
A tick in the yes box proves nothing on its own, so match each important yes to a document. With our document collection, a form answer can trigger that request. A vendor that says it will hold personal data can then be asked for the processing agreement.
Check each document before you accept it:
|
Proof document |
What it shows |
Check before you accept |
|---|---|---|
|
SOC 2 report or ISO/IEC 27001 certificate |
An independent review of security |
Recent, covers your service, names the contracting company |
|
Data processing agreement and subcontractor list |
Who handles your personal data |
Every subcontractor named, signed by the contracting company |
|
Latest financial statements or filed accounts |
Its finances at the last year end |
Recent, for the company you pay |
|
Business continuity plan |
How service comes back after an outage |
Recently tested, covers your service's systems |
Vendor Risk Scoring: Turn Answers Into a Rating
Each area gets a rating of low, medium or high from two questions. How likely is a problem, and how bad would it be for you?
Write down your vendor risk assessment criteria, so every reviewer applies the same test to every vendor. Rate each area twice, before any proof arrives and again after you check it. An area that still rates high on the second pass needs a fix written into the contract, or a decline.
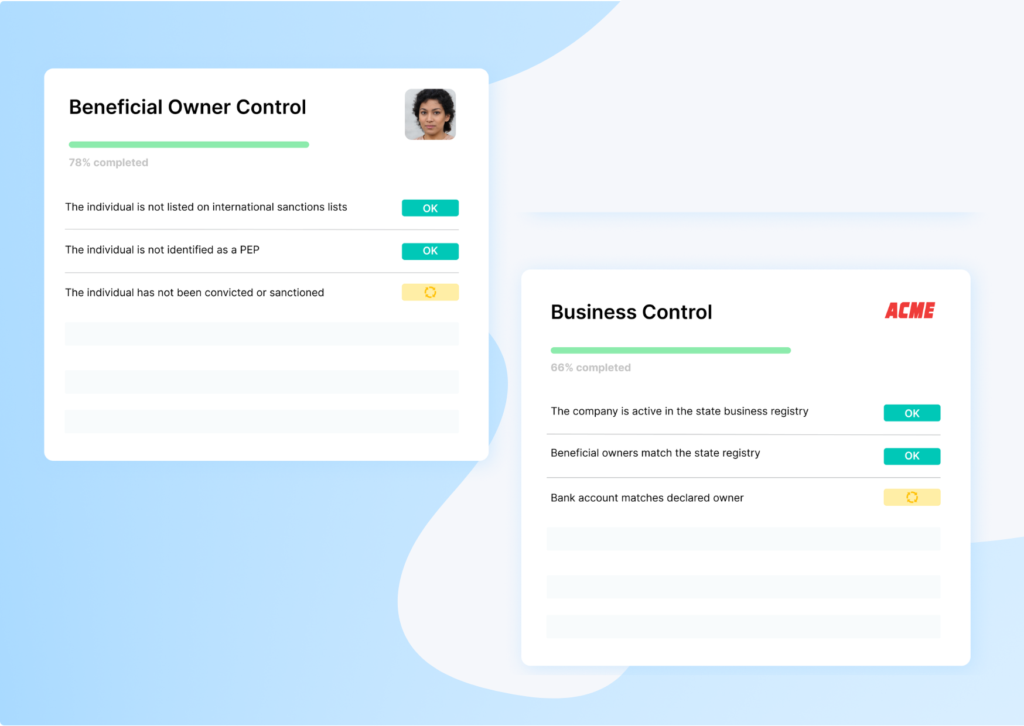
Our scoring models can do that first pass: they score a vendor's form answers against rules you set. A score can notify the people you choose and assign them a review task.
A simple rule is to give the vendor its highest area rating. A payroll provider with strong finances but full access to salary data is still high risk. If one vendor sells you several services, rate each one and then the whole relationship, because the risks add up.
What to Do With the Findings
The business wants this vendor, but its audit report covers a different service from the one you buy. What now?
You can accept the vendor, decline it, or accept it with fixes written into the contract. Each fix gets an owner and a date, agreed before anyone signs. That is vendor risk mitigation.
Here, the contract could require the vendor's next audit to cover your service by a set date.
For a high-risk vendor, procurement, IT security and legal or compliance usually each sign off. Keep a vendor risk assessment report on file: who reviewed, what proof they saw, the ratings, the decision, any conditions and the date.
Our approval workflow holds a file until the required information is in, then routes it to each approver by your rules. If an approver misses a due date, it can notify a backup approver or escalate the request.
When to Reassess a Vendor
Our vendor onboarding process guide suggests re-checking low-risk vendors at contract renewal, medium-risk once a year and high-risk twice a year.
In our platform, you can schedule compliance updates that request renewed documents automatically, such as next year's audit report. It can also ask the vendor for an update when information on file expires.
Some events should not wait for the next date. Repeat the vendor risk assessment process when:
- The vendor takes on new work, gets more access or will hold new kinds of data
- The vendor changes owner, merges or moves your contract to another company
- A breach, a long outage or a regulator action hits the vendor
- The vendor adds a subcontractor or moves to a new hosting provider
- An audit report, certificate or license expires
- The vendor's latest financial statements show its finances getting worse
Where the Assessment Fits in a Vendor Risk Management Program
Accounts payable can list every vendor it paid this year, so compare that with your vendor list. Any vendor nobody has assessed is a gap in your vendor risk management. Our vendor onboarding software keeps vendor records in one place, with an audit trail and real-time record history.
Vendor risk management covers the whole relationship: vendor list, tiers, contracts, reviews and offboarding. Vendor due diligence is the research before you sign, and the assessment uses it to rate the risk. Your written tiers, criteria and triggers make up your vendor risk management framework.
For EU financial firms and US banks, supervisors expect this too. Firms covered by DORA must assess ICT providers before signing (Article 28(4)).
In the US, the Federal Reserve, the FDIC and the OCC issued the Interagency Guidance on Third-Party Relationships: Risk Management in 2023. In September 2026, they and the National Credit Union Administration proposed new guidance that would replace it once final.
When a contract ends, remove the vendor's access and get your data returned or deleted.
Is a vendor waiting on your sign-off now? Book a demo call and walk through its questionnaire, proof files and approvals with us on one Clustdoc record.
Frequently Asked Questions
What is a vendor risk assessment?
A vendor risk assessment checks what could go wrong if a supplier fails, leaks data or breaks a rule. You run it before signing and while you work together, then decide if its controls are good enough.
What are some examples of vendor risk?
A cloud provider leaks your client files, or goes offline for a day. A subcontractor you never approved handles your customers' data. Or a key supplier goes out of business or loses a license, and your work stops.
What is a vendor questionnaire?
A vendor questionnaire is the set of questions a business sends a supplier before signing, about its company, finances, operations and data protection. In Clustdoc, an answer can trigger a request for the document behind it, such as an audit report.
Which vendors need a risk assessment?
Every vendor needs a light check, such as confirming the company exists. The full assessment is for vendors that hold personal data or client files, or can reach your systems. It also covers vendors whose failure would stop your work or affect customers.